Service 04 — Governance & Training

Make AI a capability you own — not a risk you carry.

We help you establish the policies, guardrails, and staff training that let your team innovate confidently — so AI becomes a capability your organization owns, not a risk it carries.
AI acceptable-use policyNIST AI RMFRole-based trainingOngoing review
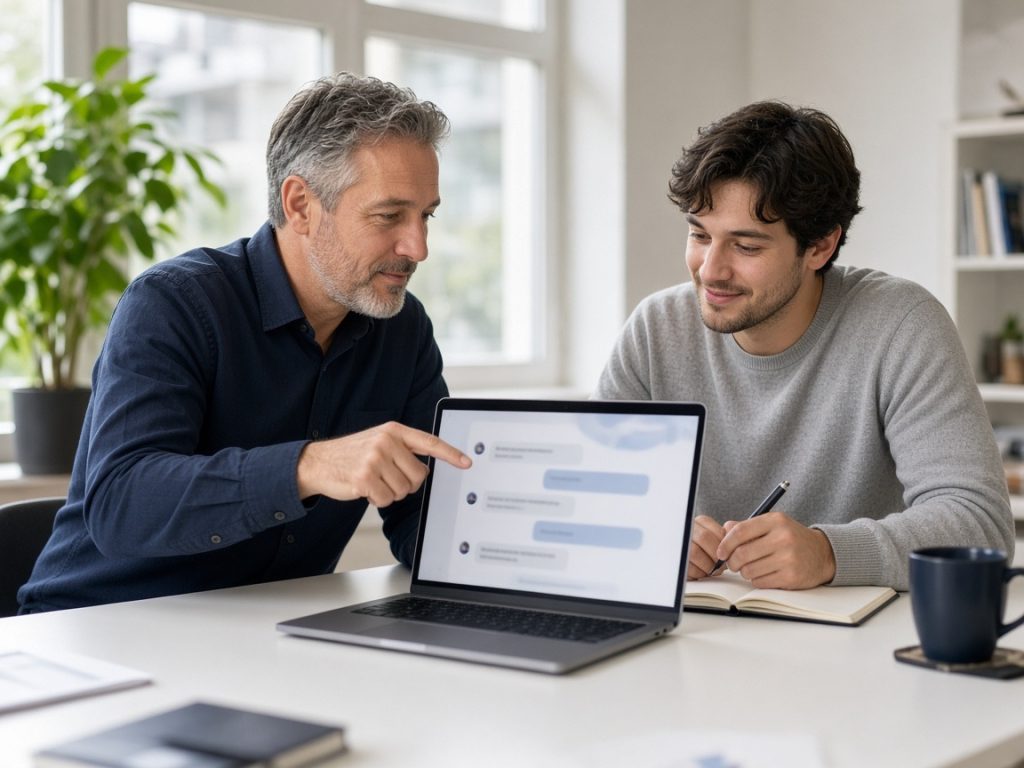
Manager coaching an employee on using an AI assistant responsibly
The outcomeA team that uses AI confidently, consistently and within clear guardrails.
Why governance matters now

Your people are already using AI. The question is how.

Whether or not AI has been formally approved, employees are experimenting with it. Governance doesn't slow that down — it channels it into tools and practices that are safe, consistent and productive.

i.

Shadow AI is the default

Without approved tools and clear rules, staff fill the gap with whatever is free and convenient — often with your data.

ii.

Policy lags behind tools

AI capabilities change monthly. Governance needs an owner and a review cadence, not a one-time memo.

iii.

Skills drive results

The difference between AI that disappoints and AI that delivers is usually how well people know how to use — and verify — it.

A recognized framework

Governance built on the NIST AI RMF.

We structure your AI governance around the four functions of the NIST AI Risk Management Framework — scaled to the size of your organization, so it's practical rather than bureaucratic.

Function 01

Govern

Set policy, roles and accountability. Establish an AI owner or steering group, an acceptable-use policy and decision rights for approving new tools.

Function 02

Map

Understand where and how AI is used — the tools, the data they touch, the people affected and the context each use case operates in.

Function 03

Measure

Assess and track risks and performance — accuracy, security, bias and business value — with metrics that are reviewed on a schedule.

Function 04

Manage

Prioritize and act on risks, respond to incidents, retire tools that no longer fit and continuously improve your controls.

NIST
AI RMF
Your governance toolkit

Practical guardrails, ready to use.

Written in plain English, tailored to your organization, and designed to be followed — not filed away.

AI acceptable-use policy

What's allowed, what isn't, and how to handle sensitive information — clear enough for every employee.

Approved tools & request process

A vetted list of sanctioned AI tools and a simple path for teams to request new ones.

AI risk register

Documented AI risks, owners and mitigations — integrated with your broader risk and compliance program.

Roles & accountability

Who owns AI decisions, who approves tools, and who reviews outcomes — defined and agreed.

Data handling rules for AI

Which data classifications may be used with which tools — including clear rules for CUI and client data.

Review cadence

Scheduled reviews as tools, risks and regulations evolve — so governance stays current.

Role-based training

The right skills for every seat.

Generic AI training doesn't stick. We tailor content to each audience — what they need to know, the tools they'll use and the risks that matter in their role.

Track 01 · Leadership

AI for decision-makers

A strategic briefing on what AI can and can't do, where it creates value, the risks leaders are accountable for, and how to oversee AI investments.

  • AI opportunities and limits, in plain English
  • Risk, liability and regulatory landscape
  • Oversight questions to ask of any AI initiative
  • Setting goals, budget and ownership
Track 02 · Managers

Leading AI-enabled teams

Practical guidance for identifying opportunities in your team's work, setting expectations, reviewing AI-assisted output and championing adoption.

  • Spotting high-value use cases in daily work
  • Quality review of AI-assisted output
  • Coaching teams through change
  • Applying the acceptable-use policy
Track 03 · Everyone

Using AI safely and well

Hands-on training with your approved tools: how to write effective prompts, verify answers, protect sensitive data and recognize AI-enabled scams.

  • Effective prompting with approved tools
  • Verifying accuracy and citing sources
  • What data never goes into AI
  • Recognizing AI-powered phishing and deepfakes
Track 04 · Technical

Administering AI securely

Deeper training for IT staff and power users on configuring, monitoring and supporting AI platforms within your security and compliance requirements.

  • Secure configuration of AI services
  • Permissions, labels and DLP for AI
  • Monitoring usage and investigating alerts
  • Building safe automations and agents
How it works

From ad-hoc to governed.

A practical path that meets you where you are today — whether AI is banned, booming, or somewhere in between.

01

Discover current use

Understand which AI tools are in use today, by whom, and with what data.

02

Draft guardrails

Policy, approved tools, data rules and roles — reviewed with your leadership.

03

Train & launch

Role-based training and a clear rollout so everyone knows the rules and the tools.

04

Review & evolve

Scheduled reviews keep policy, tools and skills current as AI changes.

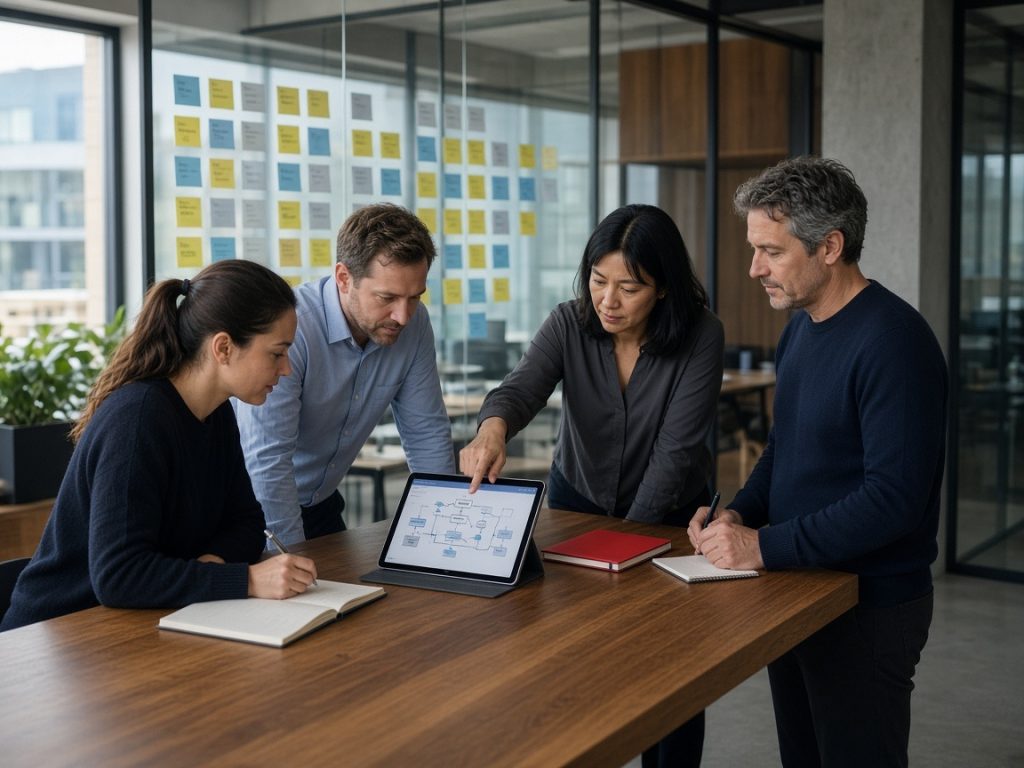
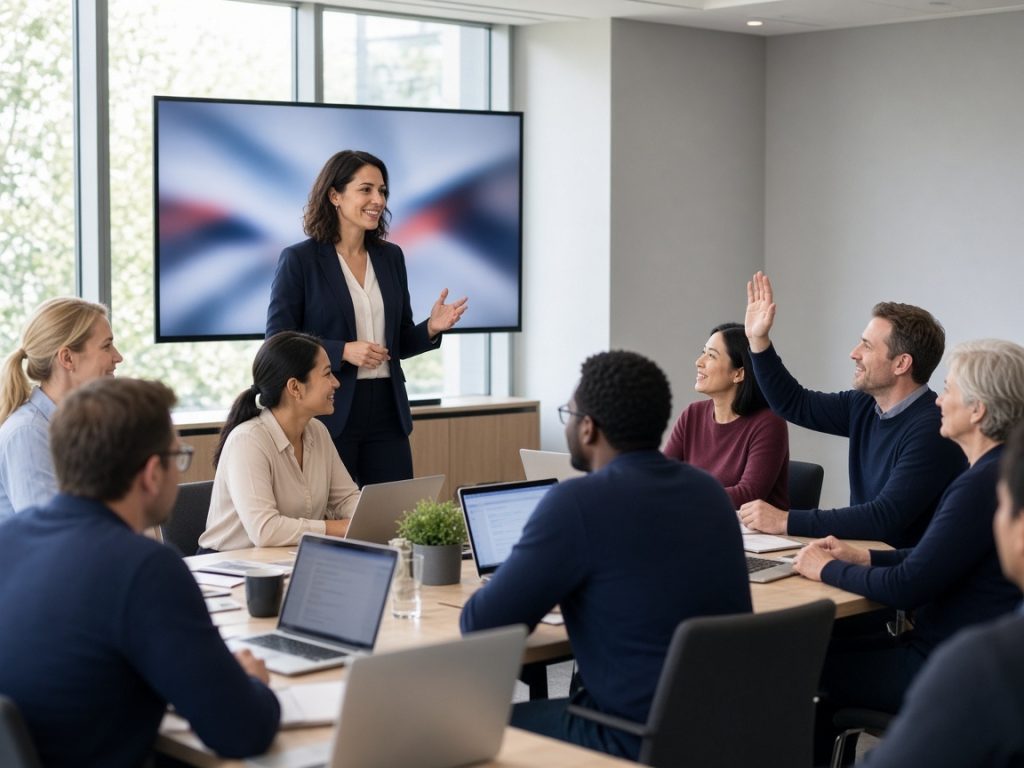
Employees engaged in an AI governance training workshop
Confidence, not fearTeams that know the rules innovate faster.
The outcome

Innovation with guardrails your whole organization understands.

Good governance is what lets you say "yes" to AI more often. With clear rules, trusted tools and trained people, your organization can move quickly without wondering what's happening to its data.

  • Reduced shadow AI and data exposure
  • Consistent, higher-quality AI output
  • Faster, safer adoption of new tools
  • Evidence of responsible AI for clients and auditors
Governance FAQ

Governance, demystified.

We're a small organization. Do we really need AI governance?
Yes — but scaled to your size. For many organizations that means a clear acceptable-use policy, an approved tools list, a named owner and practical training. We right-size governance so it protects you without creating bureaucracy.
What is the NIST AI Risk Management Framework?
The NIST AI RMF is a voluntary framework from the National Institute of Standards and Technology for managing AI risks. It is organized into four functions — Govern, Map, Measure and Manage — and provides a credible, widely recognized structure for AI governance.
Is training delivered in person or online?
Both. We offer live workshops on-site in the D.C. metro area or virtually, and can provide recorded refreshers and quick-reference guides so new hires get the same foundation.
How often should our AI policy be updated?
We recommend a scheduled review at least annually, plus updates whenever you adopt a significant new tool, your regulatory obligations change, or an incident reveals a gap.
Explore the practice

One partner for every stage of AI adoption.

Each service stands on its own, and they are designed to work together — from first assessment to a governed, secure AI capability your organization owns.
Schedule an AI Readiness Consultation

Give your team the confidence to innovate safely.

Start with a conversation. In a no-obligation AI Readiness Consultation, we will listen to your goals, ask about your data and security requirements, and outline practical next steps — whether that is an assessment, a pilot, or simply a clearer picture of where AI fits.

Call our team(571) 540-7107 Emailinfo@solvereone.com
OfficesDulles, VA  ·  Washington, DC

Request your consultation

Tell us a little about your organization. A member of our AI practice will reach out within one business day.

We respect your privacy. Your information is used only to respond to your request.